Jonathan Chee
Penetration tester and security engineer. I break web apps, APIs and internal networks, and build tools that optimise my workflow with AI.
- Document
- Portfolio
- Prepared by
- Jonathan Chee
- Scope
- Offensive security, tooling
- Based in
- Singapore
- Credentials
- 8 certifications
- Classification
- PUBLIC
- CV
- Available on request
Summary
I run penetration tests and red team engagements across web, API, mobile, network, wireless, cloud and thick-client targets, and build tools that optimise that workflow with AI. The latest is AEGIS, a workbench that lets an AI assistant help on real engagements without ever seeing a real client value.
- Penetration testing
- Web applications, APIs, mobile (iOS and Android), thick clients, internal and external networks, Active Directory, cloud, wireless, red team
- Assessments
- Network vulnerability assessments
- Experience
- 7+ years in cybersecurity, 3+ in penetration testing and red teaming; 75+ engagements
Credentials
- OSCP
- OSWE
- OSEP
- CRTO
- CRTP
- CREST CPSA
- CREST CRT
- BSCP
- Type
- Tool, flagship
- Platform
- Windows, local-first
- Source
- Private
AEGIS v2
A local-first pentest workbench that runs an engagement end to end, with Claude Code docked inside it. Claude reaches engagement data only through a masking boundary, so it never sees who the client is.
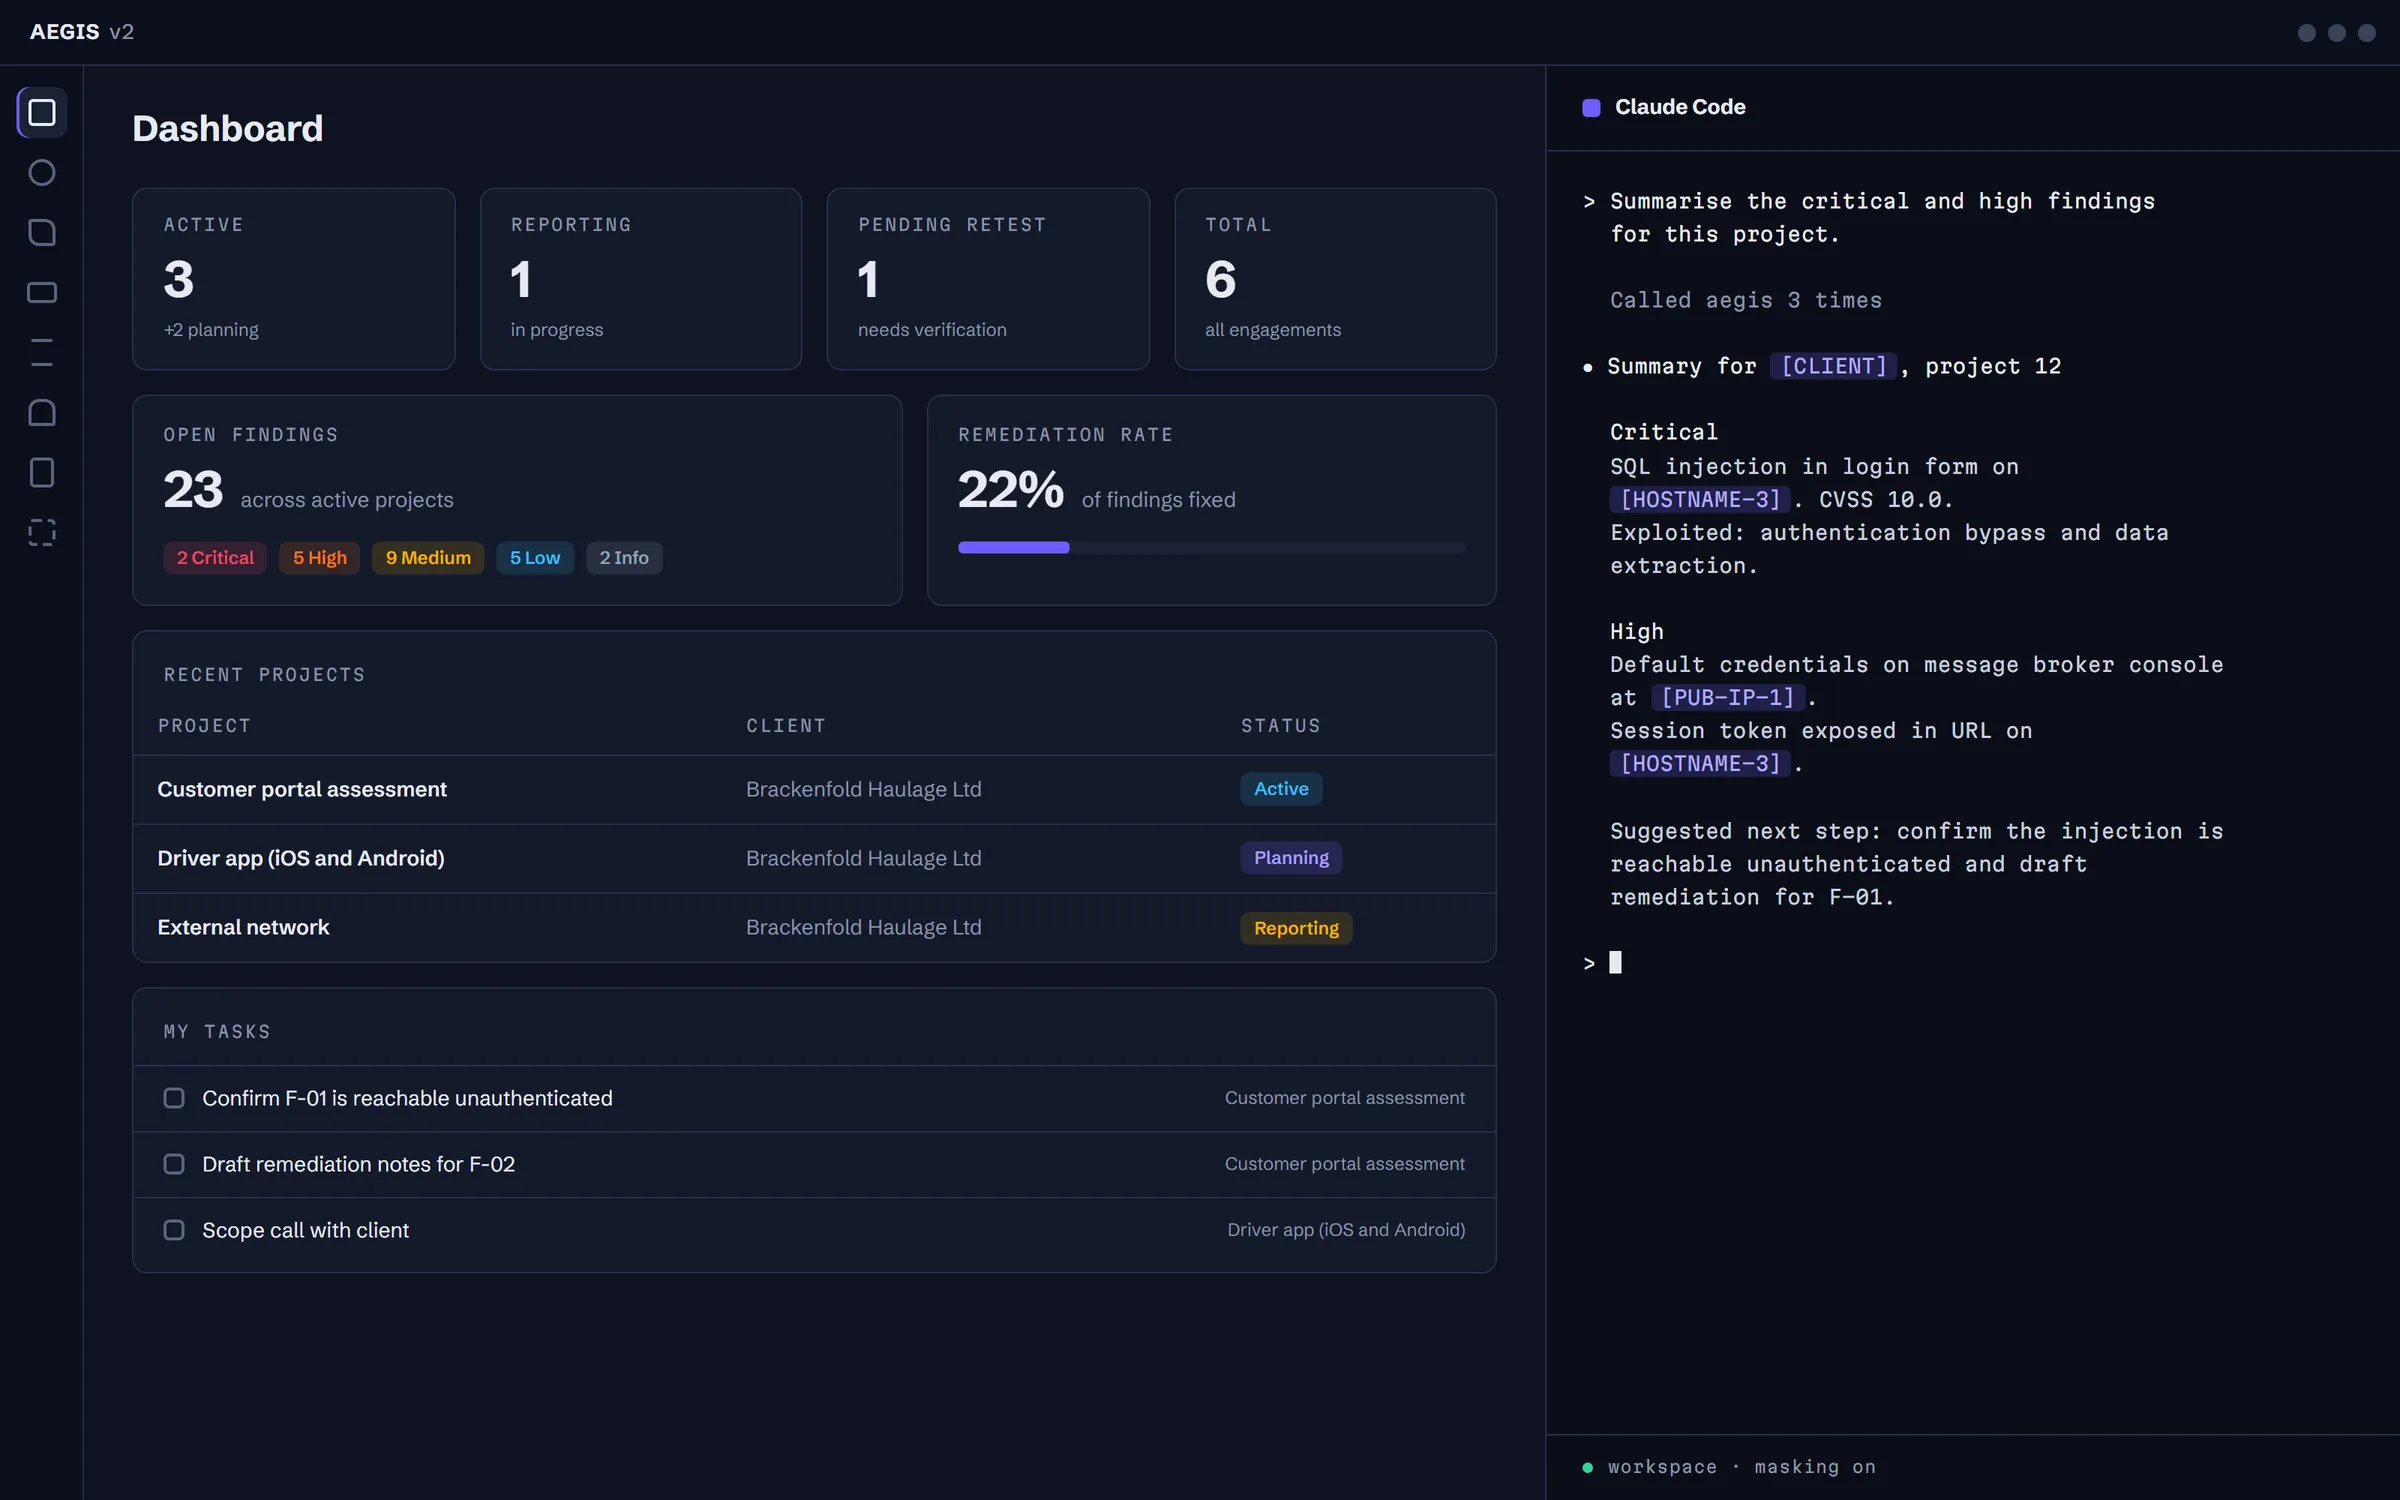
One finding, two views
| Client | Brackenfold Haulage Ltd |
|---|---|
| Host | portal.brackenfold.example |
| Public IP | 203.0.113.45 |
| Note | TLS 1.0 still enabled on 203.0.113.45 |
| Unmasked value | Response withheld. Nothing crosses unmasked. |
- Local-first
- Engagement data lives on the operator's machine. Nothing is synced anywhere by default.
- Fail-closed masking
- Every tool response is scanned before it leaves AEGIS. If a real value slipped past the mask, the whole response is withheld.
- Burp without the setup
- The SSH tunnel to a remote Kali box is managed for you. It is a separate, opt-in channel and is not masked.
- Employers
- Redacted by design
Experience
| Years | Role | Employer |
|---|---|---|
| 2026-present | Senior Consultant, Penetration Testing Leads web, API, mobile, network, Active Directory and cloud tests for aviation, financial-services and other regulated clients. Built Frida tooling to automate iOS assessments. [EMPLOYER_01] | [EMPLOYER_01] |
| 2024-2026 | Cybersecurity Consultant, Penetration Testing Close to 60 engagements across web, mobile, API, network and wireless, plus an assumed-breach red team engagement. [EMPLOYER_02] | [EMPLOYER_02] |
| 2018-2024 | Cybersecurity Engineer, Team Lead Led a four-person SIEM/SOAR team (IBM QRadar, Sumo Logic); moved into penetration testing in the final year. [EMPLOYER_03] | [EMPLOYER_03] |
Latest write-ups
| Date | Entry | Read |
|---|---|---|
| 2026-10-03 | I passed OSEP on my first attempt with 15 flags. Notes on how I studied, how the two days went, and whether PEN-300 is worth it. | 4 min |
| 2026-10-03 | I passed OSWE on my first attempt, both targets fully. It was the hardest OffSec exam I've done, and this is what got me through it. | 4 min |
- Channel
- Email preferred
Rules of engagement
jonathan_chee95@hotmail.com- GitHub
- github.com/jaysee95
- linkedin.com/in/jonathancheewx
- CV
- On request